

Unidentified OT assets
The true attack surface cannot be measured without a current inventory of PLCs, HMIs, drives, servers and engineering workstations.
Our OT cybersecurity solution combines passive asset discovery, risk analysis, zone–conduit segmentation, secure remote access, continuous monitoring and incident response with production continuity.
Explore the solution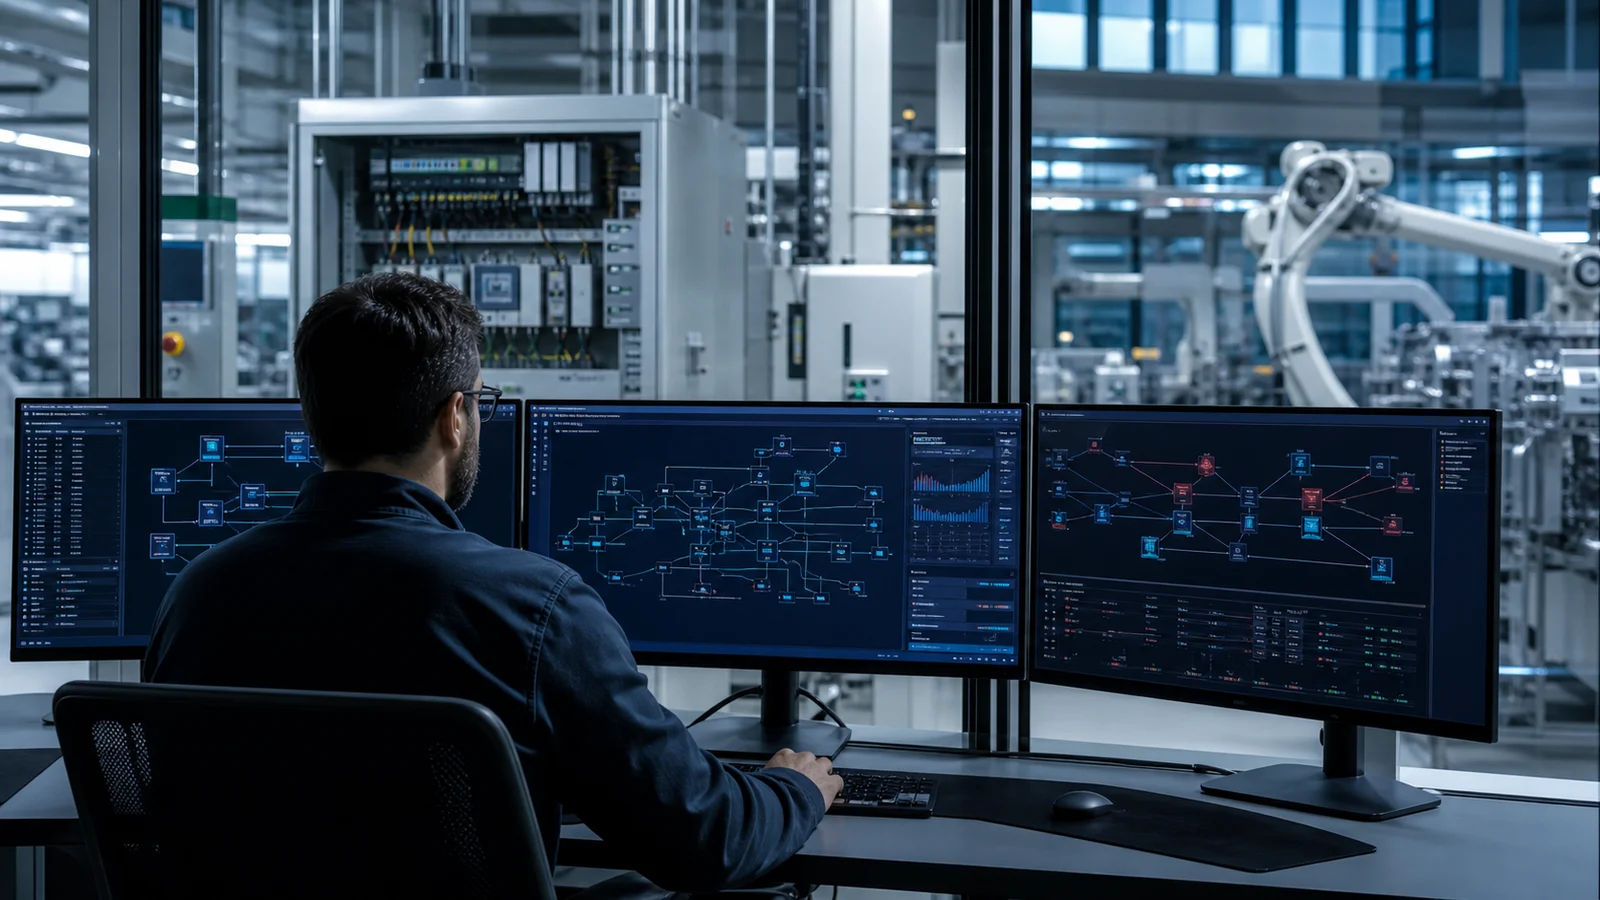
The true attack surface cannot be measured without a current inventory of PLCs, HMIs, drives, servers and engineering workstations.
Unsegmented cells allow a single incident to spread into critical production areas and across plant zones.
Supplier and maintenance connections create a persistent attack surface without identity verification, approval, time limits, authorisation and session recording.
OT security combines asset discovery, zone–conduit segmentation, secure remote access, threat monitoring and incident response within one operating model.
Rather than passing directly from the enterprise network to a field cell, traffic moves layer by layer through controlled conduits. Unauthorised flows are blocked at the boundary and approved sessions are recorded.
Controls are translated into a practical roadmap that reflects the plant architecture and maintenance realities.
OT devices, software versions, protocols and inter-system traffic are mapped using passive methods.
Asset importance, process impact, exposure and existing controls are assessed together.
Functional cells are separated by boundaries that permit only required services and flows.
Maintenance access is controlled through multifactor authentication, approval, time-limited authorisation and session recording.
New devices, unexpected commands, out-of-policy traffic and behavioural changes are monitored.
OT incident scenarios, backup, recovery and responsibilities are validated through tabletop and field exercises.
The OT network is monitored passively, comparing device relationships, protocols and critical changes over time so teams can act on contextualised incidents rather than raw alerts.
Production areas, critical processes, owners and acceptable downtime limits are defined.
Devices, protocols, connections and existing security controls are made visible.
Technical findings are combined with process impact to create a practical remediation sequence.
Segmentation, secure access, hardening and backup controls are implemented.
Anomaly rules, escalation paths and OT-specific incident response procedures are operated.
Controls are reviewed regularly through exercises and change records.
Protection of PLCs, HMIs, SCADA, robots and production cells through a controlled network architecture.
Access and incident visibility across electrical, steam, water, gas and energy-management systems.
Time-limited, approved, traceable and recorded access for OEM and service teams.
Scalable management through common standards, central visibility and site-level ownership.
Customer and facility information has been anonymized to meet confidentiality obligations.
Share your current architecture and priority risks with the team specialising in industrial cybersecurity.
Request an OT security assessment Your request is routed directly to the relevant engineering team.
Engineering confidence with Oskon.
Leave your details and our expert engineers will contact you for a preliminary consultation tailored to your needs.